Think about how you double-check that your front door is locked before heading to bed, or how a professional locksmith tests a lock to make sure it is truly secure. That is essentially what ethical hacking is. Rather than breaking into websites to steal data, you are actually helping companies find the “unlocked doors” in their digital systems so they can fix them before a real attacker does. For anyone into tech, it is a hands-on way to learn exactly how computers, networks, and apps work—and more importantly, how to shield them. Ethical hacking for students is a growing field, offering exciting opportunities to learn and protect digital systems. However, becoming a pro takes more than just a few fancy tools. You need a solid grasp of the basics, from operating systems to networking and core security principles.
Most importantly, you have to understand the line between helpful and illegal. Just as a locksmith would not pick a random stranger’s lock for fun, an ethical hacker only works in environments where they have explicit permission. It is about mastering the art of the break-in to ensure a malicious break-in never happens.
Ethical hacking connects with several important areas of cybersecurity, including:
- Network Security — protecting networks and communications from unauthorized access and attacks.
- Encryption — protecting information by transforming it into a form that unauthorized users cannot easily understand.
- Malware — understanding malicious software and how it can compromise systems.
- Threat Intelligence — analyzing information about threats and attacker behavior.
- Cloud Security — protecting cloud-based applications, infrastructure, and data.
- Incident Response — detecting, containing, and recovering from security incidents.
What Is Ethical Hacking and Why Does It Matter for Students?
Defining Ethical Hacking in Simple Terms
Ethical hacking means testing computer systems for security weaknesses, but only with permission. Professionals known as ethical hackers or white-hat hackers use the same techniques as malicious attackers, but they have legal approval from the system owner. Their main goal is to find and fix problems before real attackers can take advantage of them. This work is also called penetration testing or a security assessment. According to CISA, cybersecurity is about protecting systems, networks, and programs from digital attacks, unauthorized access, and damage (CISA, 2023). Ethical hackers look for security gaps before anyone else finds them. Today, many organizations need penetration testing to follow compliance rules. If students learn about ethical hacking early, it can give them a professional edge. Above all, ethical hacking means protecting people and systems, not causing harm.
Why This Skill Is Especially Relevant Today
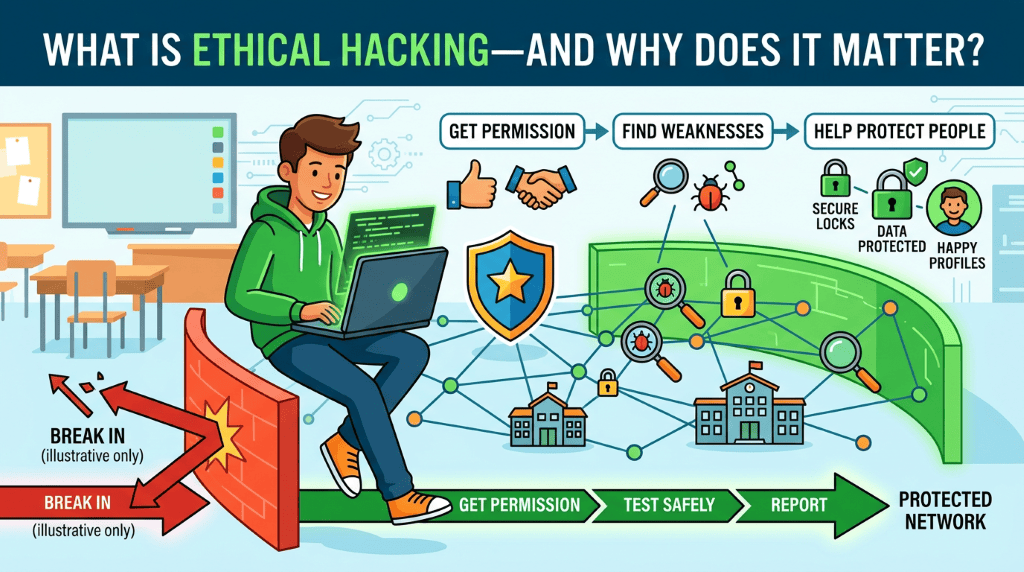
Today, cybercrime damages are projected to reach trillions of dollars annually. The Verizon 2026 DBIR confirms that human error and unpatched vulnerabilities remain the top two causes of data breaches globally. As a result, organizations urgently need trained professionals. A key gap is that millions of cybersecurity positions remain unfilled worldwide.

Anyone who decides to study this subject today may look forward to good job prospects. In addition, governments are investing resources in cybersecurity education in order to enhance their national defence. The demand for qualified security professionals does not remain limited to technology companies. Fields such as healthcare, finance, education and government all depend on these specialists.
As students currently make frequent use of digital tools, they already have practical experience which can be developed through formal cybersecurity training. The fact that there is this link with real-world experience means that ethical hacking has become one of the most valuable skills for students to learn at this time.
Cybersecurity vs. Information Security vs. Network Security: What Is the Difference?
Understanding these three terms helps students choose the right specialization. While people may use them interchangeably, each has a distinct meaning.
Here are clear definitions for each term:

Cybersecurity means protecting internet-connected systems—like hardware, software, and data—from digital attacks and unauthorized access. It deals mainly with threats that come from cyberspace (CISA, 2023).
Information security covers a wide range of practices to protect all kinds of information, whether digital or physical, from being accessed, changed, or destroyed without permission. It uses different policies, processes, and technologies to keep information safe in any form.

Network Security: A subset of cybersecurity focused specifically on protecting the integrity, confidentiality, and availability of computer networks and the data transmitted across them.
This distinction matters for students planning their studies. For instance, a student interested in firewalls and protocols will lean toward Network Security. A student drawn to policy and data governance will lean toward Information Security. Those who enjoy hands-on technical testing often find cybersecurity and ethical hacking most exciting.
What Are the Core Concepts Every Student Needs Before Starting Ethical Hacking?
Building the Right Technical Foundation
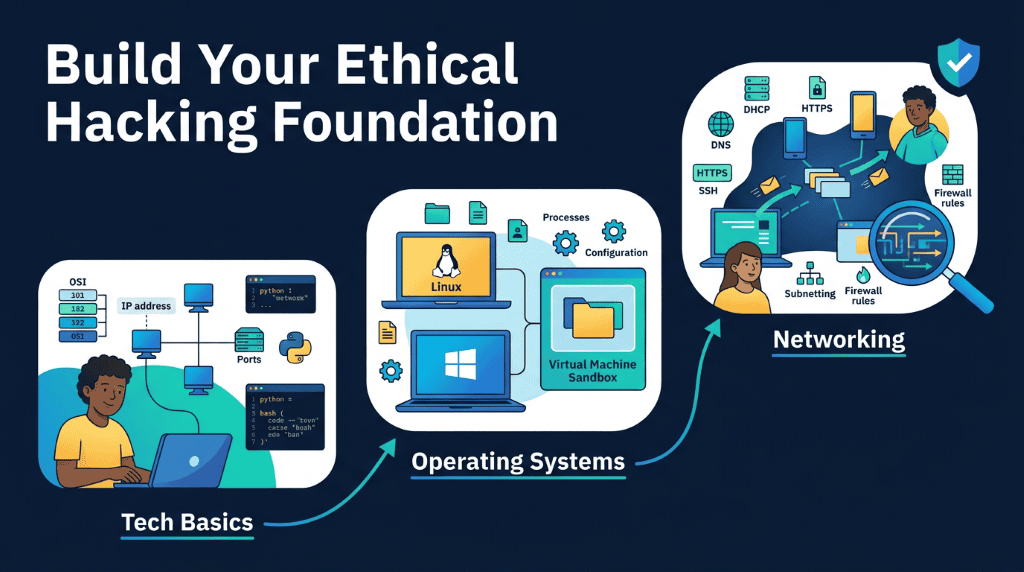
Before attempting any hacking techniques, students must understand foundational concepts. These include how networks function, basic operating system principles, and programming fundamentals. Specifically, students should be comfortable with the OSI model, TCP/IP protocols, IP addressing, and port functions. These are the building blocks of all network communication. In addition, learning at least one scripting language, such as Python or Bash, is highly valuable. Python is particularly popular in cybersecurity because of its readability and powerful libraries. A study published in a Springer journal confirms that foundational technical education significantly improves student outcomes in security training (Cheng et al., 2019). As I have noted, students who skip the fundamentals often struggle with intermediate topics. Just as you learn arithmetic before algebra, cybersecurity fundamentals come first. Starting with these concepts ensures that ethical hacking skills build on a solid base.
Understanding Operating Systems and Virtualization
Ethical hackers work across multiple operating systems. Linux is the most commonly used platform in cybersecurity work. Distributions such as Kali Linux come pre-installed with hundreds of security testing tools. Students should install Kali Linux in a virtual machine environment on their computers. Virtualization tools such as VirtualBox or VMware allow students to practice safely. They can test attack and defense techniques in isolated environments. This approach protects their main systems from accidental damage. At the same time, knowledge of Windows and macOS is also useful. Many real-world targets run Windows systems. Understanding Windows Active Directory, for example, is critical for many penetration testing scenarios. In this case, familiarity with both Linux and Windows gives students a significant advantage. Core OS skills include file system navigation, user permissions management, process monitoring, and network configuration.
The Role of Networking Knowledge in Ethical Hacking
Networking is the backbone of all cybersecurity work. Students must understand how data moves across systems. In essence, every cyberattack and every defense strategy happens at the network level. Key networking concepts include DNS, DHCP, HTTP/HTTPS, FTP, and SSH protocols. Students should also understand subnetting and firewall rules. Tools like Wireshark allow students to analyze network traffic in real time. This kind of hands-on practice is irreplaceable. The NIST Cybersecurity Framework emphasizes understanding network architecture as a core component of any security program (NIST, 2018). As professional job listings show, network analysis appears in nearly every penetration tester role description. To move forward effectively, students should master networking before advanced hacking topics, as both academic researchers and industry professionals recommend.
What Tools and Techniques Do Student Ethical Hackers Use?
Popular Tools Used in Student Cybersecurity Training
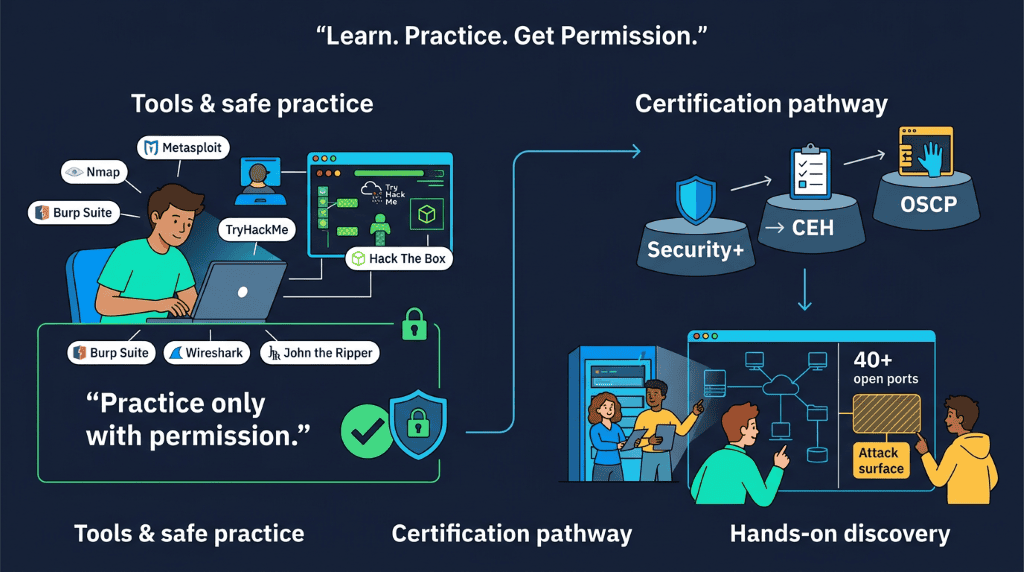
Ethical hackers use specific tools to test systems for vulnerabilities. Many of these tools are open-source and freely available. Common beginner tools include Nmap for network scanning, Metasploit for exploit testing, Burp Suite for web application testing, Wireshark for packet analysis, and John the Ripper for password testing. These tools are legal to use only in authorized environments. Students should always practice on systems they own or have explicit permission to test. Platforms like TryHackMe and Hack The Box provide legal, gamified environments. Students complete missions that simulate real-world attack scenarios. Using these platforms is one of the safest and most effective ways to build practical skills. As I have said, the key difference between ethical hacking and criminal hacking is always consent and authorization. That boundary must never be crossed.
Cybersecurity Certifications That Students Can Pursue
Certifications validate students’ skills for potential employers. At first, students often target entry-level certifications to build credibility. The most recognized entry-level certification is the CompTIA Security+. This certification covers network security, threats, cryptography, and compliance. After that, students often progress to the Certified Ethical Hacker (CEH) certification by EC-Council. The CEH teaches systematic penetration testing methodologies. For advanced learners, the Offensive Security Certified Professional (OSCP) is the gold standard. OSCP requires students to compromise multiple systems in a live exam environment. Put differently, it tests real skill, not just memorization. IEEE research confirms that structured certification pathways significantly improve cybersecurity workforce readiness (Sridhar et al., 2015). Secondary- and undergraduate-level students can start with Security+ and build up. Each certification opens new career doors.
A Classroom Observation Worth Sharing
During a cybersecurity workshop I facilitated with undergraduate students, one exercise stood out clearly. Students were asked to scan a virtual network using Nmap and identify open ports on a test server. Initially, most students expected to find one or two open ports. Instead, they discovered over forty open ports on a poorly configured practice machine. Suddenly, the abstract concept of an “attack surface” became very real. Several students asked, “Is this what real corporate systems look like?” The answer, unfortunately, is often yes. In fact, the Verizon 2026 DBIR highlights that misconfigured systems remain among the top causes of breach incidents. That moment of discovery changed how those students approached their learning. To show the power of hands-on labs, this direct experience builds intuition that reading alone cannot replicate.
How Can Students Practice Ethical Hacking Legally and Responsibly?
Setting Up a Safe Home Lab Environment
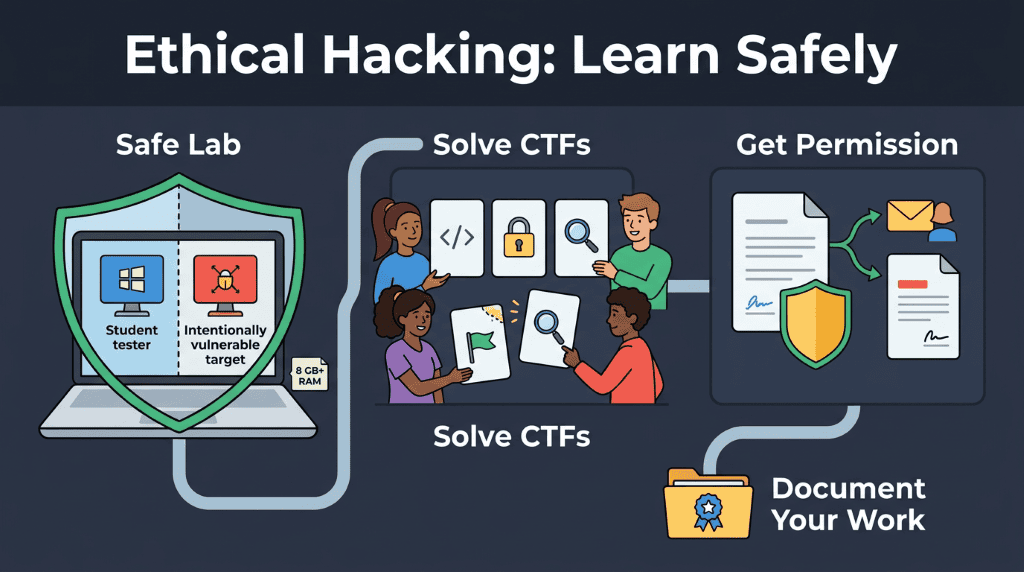
Students do not need expensive hardware to start practicing. A standard laptop with at least 8 GB of RAM can run multiple virtual machines. VirtualBox is free and supports multiple OS installations. Students can set up a home lab with one Kali Linux attacker machine and one intentionally vulnerable target machine. Projects like Metasploitable and DVWA (Damn Vulnerable Web Application) are specifically designed for ethical hacking practice. These are legal, intentionally broken systems built for students to attack. Similarly, setting up a home lab teaches skills like network configuration and system administration alongside hacking techniques. The Springer-published Cybersecurity journal outlines the importance of practical lab environments in developing effective cybersecurity professionals (Cheng et al., 2019). Moreover, this self-directed learning shows initiative to future employers. Building a documented home lab portfolio is an excellent addition to any student’s resume.
Online Platforms and Capture the Flag Competitions
Capture the Flag (CTF) competitions are one of the best learning methods available to students. In a CTF challenge, participants solve puzzles that involve hacking, cryptography, reverse engineering, and forensics. Each solved challenge reveals a “flag,” which is a specific piece of text that confirms success. Platforms like PicoCTF are specifically designed for high school students. CTFtime.org lists competitions worldwide. Students can join CTFs on their own or with a team.
Taking part in these competitions helps you think quickly, solve problems creatively, and build technical skills all at once. Employers in cybersecurity often look for CTF experience on resumes because it shows you have hands-on skills, not just classroom knowledge. According to research in IEEE, learning through games and competition helps students remember technical cybersecurity concepts much better (Sridhar et al., 2015). CTFs are still one of the most interesting and effective ways for students to build their cybersecurity skills.
Legal and Ethical Boundaries Every Student Must Know
Ethical hacking comes with clear legal limits. In the United States, the Computer Fraud and Abuse Act (CFAA) makes it a federal crime to access computers without permission. Other countries, like India and the UK, have similar laws. Students should never test or scan systems unless they have written permission. This rule applies everywhere, whether you are at home, at school, or anywhere else. Always use practice platforms or your own devices for learning. Respecting privacy is just as important. Ethical hackers do not keep, share, or misuse any data they find during testing. Responsible disclosure means reporting any security issues to the system owner before telling others. Both the NIST Cybersecurity Framework and CISA highlight responsible disclosure as a key professional standard (NIST, 2018; CISA, 2023). If students stick to these guidelines, their hacking practice will stay legal and ethical
What Career Paths Open Up with Ethical Hacking Skills?

Cybersecurity Career Roles That Value Hacking Skills
Ethical hacking skills open doors to many career paths. The most direct role is a penetration tester, also called a pen tester. Penetration testers simulate attacks on client systems to find vulnerabilities. Another key path is a vulnerability analyst. These professionals assess software and systems for known security weaknesses. Red Team specialists simulate sophisticated, long-term attack campaigns against organizations. Blue Team defenders monitor, detect, and respond to real attacks. Additional career options include security operations center (SOC) analyst, malware analyst, threat intelligence specialist, cloud security engineer, and incident response analyst. Each of these roles values the skills built through ethical hacking training. Research in the International Journal of Information Security confirms that technical hacking experience is one of the strongest predictors of cybersecurity career success (Bulgurcu et al., 2010). All things considered, ethical hacking is one of the most career-relevant skills a student can develop in the digital age.
Salary Ranges and Job Market Data
The cybersecurity job market is very strong right now. In the United States, entry-level roles like SOC analyst usually pay between $55,000 and $75,000 a year. Penetration testers with a few years of experience can earn $90,000 to $130,000, while senior red team specialists and security architects often make more than $150,000. Because there is a global shortage of skilled workers, experienced professionals are in high demand. The Verizon 2026 DBIR notes that many successful breaches happen because security teams are understaffed, which shows how urgently trained talent is needed. Besides good pay, people in cybersecurity often have the option to work remotely, keep learning new skills, and report high job satisfaction. Overall, this field offers strong financial and professional rewards. Students who start learning about cybersecurity early can set themselves up for long-term career success.
How Ethical Hacking Builds Transferable Skills
Ethical hacking does more than get students ready for cybersecurity jobs. It helps them build skills they can use in many careers. Problem-solving stands out as one of the most important. Ethical hackers need to think in new ways about how systems might break down. This kind of thinking is useful in software engineering, systems design, and business strategy. Security training also helps students develop critical thinking and attention to detail.
According to a study in the Journal of Adolescent Health, structured technical training programs improve cognitive flexibility and analytical reasoning in adolescents (Valkenburg & Patti, 2018). Ethical hacking also instills patience and persistence, since it is not uncommon for penetration testing to require several attempts before a vulnerability is discovered. The development of these qualities assists students in achieving success in any technical or analytical area.
Therefore, education in ethical hacking is not merely about preparing people for a job; it is a demanding field of study which, in the long term, enables students to think more clearly.
What Resources and Roadmaps Help Students Learn Ethical Hacking Systematically?
Structured Learning Roadmaps for Beginners
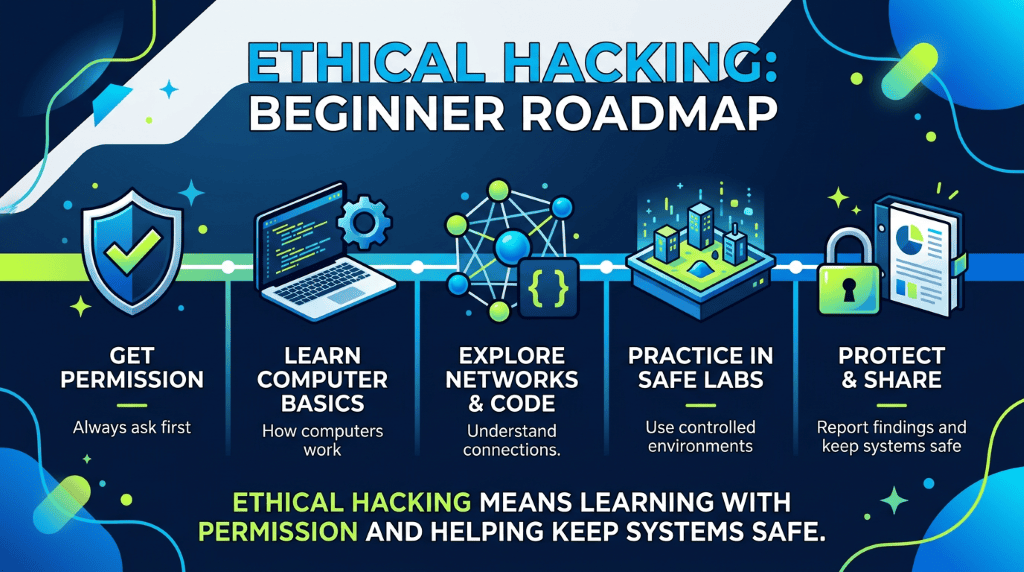
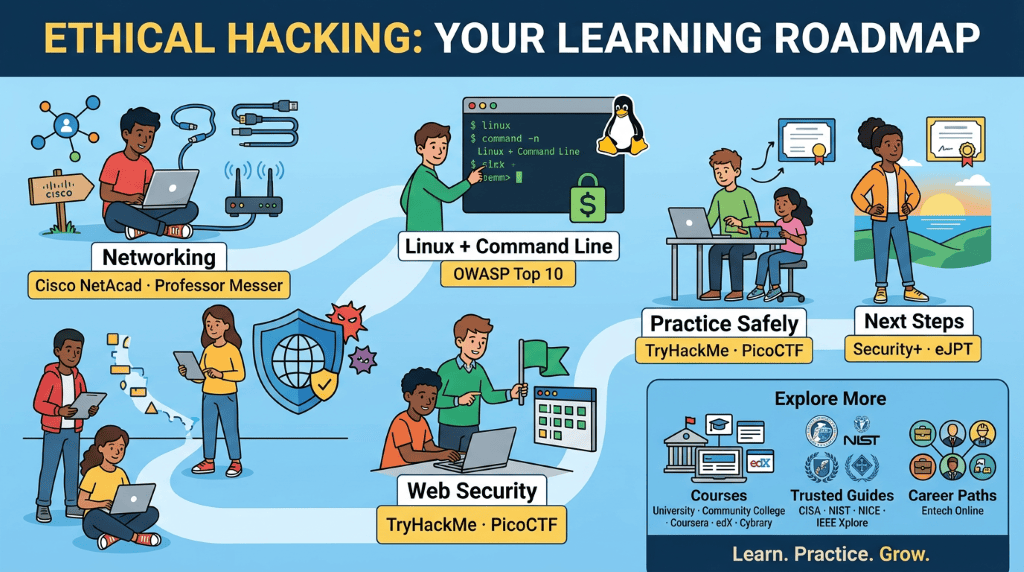
Students often feel overwhelmed by the breadth of cybersecurity topics. A structured roadmap prevents this. Start with networking fundamentals using free resources like Cisco’s NetAcad or Professor Messer’s free CompTIA materials. Start by learning the basics of Linux and getting comfortable with the command line. After that, check out OWASP’s free Top 10 documentation to learn about web application security. Practice your skills on platforms like TryHackMe or PicoCTF. When you feel ready, consider earning an entry-level certification such as CompTIA Security+ or the eJPT from INE. This step-by-step plan helps you cover a wide range of topics and avoid missing important skills. The NIST Cybersecurity Framework is a great resource for seeing how these skills fit into a real-world security program (NIST, 2018). You can also find detailed learning paths and career advice at entechonline.com, which organizes topics from beginner to advanced.
University Programs and Online Courses Worth Exploring
Getting a formal education can help you move forward in a cybersecurity career. Many universities now have specific courses in cybersecurity and ethical hacking for both undergraduate and graduate students. Programs recognized as NSA Centers of Academic Excellence in Cybersecurity are especially well-regarded. Community colleges also provide affordable associate degrees with strong cybersecurity content. If you cannot attend a traditional program, online platforms are a great option. Coursera, edX, and Cybrary offer structured cybersecurity courses from top universities and industry experts, and many of these are free to audit. Listing these completed courses on LinkedIn can show your dedication to professional growth. According to IEEE research, students learn best when they combine online lessons with hands-on labs (Sridhar et al., 2015). You can also find more learning tools and advice for students at entechonline.com’s STEM learning hub, which is designed to support your career goals.
Free Government and Academic Resources Every Student Should Know
Several high-quality, free resources come from government and academic institutions. CISA publishes free cybersecurity advisories, training materials, and toolkits specifically designed for students and educators. The NIST Cybersecurity Framework is a free, publicly available guide that defines best practices for managing cybersecurity risk. NIST also publishes the Cybersecurity White Paper (CSWP) series, which covers cutting-edge topics like zero trust architecture and post-quantum cryptography. NIST’s NICE Cybersecurity Workforce Framework maps cybersecurity roles to specific skills and knowledge requirements. This framework helps students identify which skills to prioritize for specific career goals. In addition, IEEE Xplore offers free access to selected research papers on cybersecurity education and workforce development. Using these authoritative sources ensures that students build skills aligned with real-world professional standards. After all, learning from primary sources builds stronger knowledge than relying on secondary summaries alone.
What Ethical Responsibilities Come with Hacking Knowledge?
The White-Hat Hacker’s Code of Conduct
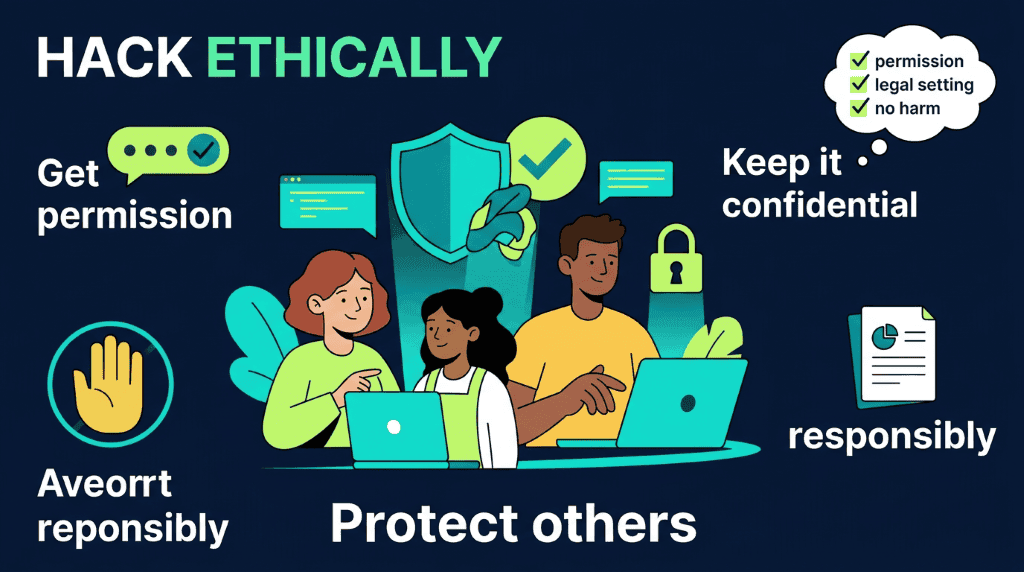
Ethical hackers follow a clear code of conduct. The first rule is authorization: always get written permission before testing any system. The second rule is confidentiality. Keep all findings private unless you report them through the proper channels. The third rule is to minimize impact, so avoid causing service disruptions or data loss during your work. The fourth rule is responsible disclosure, as mentioned earlier. These rules match the EC-Council’s official Code of Ethics for certified ethical hackers. What separates an ethical hacker from a criminal is not the tools, but the intent and permission behind each action. Research in the IEEE Security and Privacy journal shows that having clear ethical guidelines helps build trust in cybersecurity professionals (Sridhar et al., 2015). Students should learn and follow these principles from the very start of their training.
Cybersecurity, Privacy, and Student Responsibility
When students use cybersecurity tools, they take on a social responsibility. Skills like understanding malware, spotting encryption weaknesses, and knowing how to respond to incidents can be used in harmful ways. However, these skills are also crucial for protecting others and keeping communities safe. What matters most is your intent and the situation. Before using any hacking tool, ask yourself: Do I have permission? Is this a legal setting? Could I be harming anyone? These questions help you make ethical choices. Research from Tandfonline’s Journal of Adolescent Research shows that adolescents who get structured ethics education along with technical training show stronger professional integrity throughout their careers (Valkenburg & Patti, 2018). CISA’s advisory on ethical cybersecurity practices also points out that students and young professionals are responsible for keeping shared digital spaces secure (CISA, 2023). With this mindset, every ethical hacker helps protect the digital world they work in.
Frequently Asked Questions About Ethical Hacking for Students
Programming isn’t essential initially; learn networking and Linux first, then Python to automate, analyze malware, and build security tools.
Ethical hacking requires permission; practice in authorized labs, bug bounties, or your own systems—not others’ without consent.
Kali Linux or Ubuntu — explore Linux and security tools.
Wireshark — understand network traffic.
Nmap — discover devices on authorized networks.
Burp Suite Community Edition — learn web security.
VirtualBox or VMware — create isolated practice labs.
OWASP Juice Shop, DVWA, and Metasploitable — practice safely on intentionally vulnerable systems.
A computer science degree helps but isn’t required; employers value practical skills, strong fundamentals, ethical conduct, projects, and relevant certifications..
Practice safely in virtual labs with vulnerable apps and legal platforms like TryHackMe, Hack The Box Academy, PortSwigger, and OWASP.
References
Bulgurcu, B., Cavusoglu, H., & Benbasat, I. (2010). Information security policy compliance: An empirical study of rationality-based beliefs and information security awareness. MIS Quarterly, 34(3), 523–548. Cybersecurity in healthcare: A narrative review of trends, threats and ways forward – PubMed
Cheng, L., Liu, F., & Yao, D. (2019). Enterprise data breach: Causes, challenges, prevention, and future directions. Cybersecurity, 2(1), 1–16. Survey of intrusion detection systems: techniques, datasets and challenges | Cybersecurity | Springer Nature Link
Cybersecurity and Infrastructure Security Agency. (2023). What is cybersecurity? U.S. Department of Homeland Security. What is Cybersecurity? | CISA
Cybersecurity and Infrastructure Security Agency. (2023). Advisory AA23-215A: 2022 Top Routinely Exploited Vulnerabilities. U.S. Department of Homeland Security. 2022 Top Routinely Exploited Vulnerabilities | CISA
National Institute of Standards and Technology. (2018). Framework for improving critical infrastructure cybersecurity (Version 1.1). U.S. Department of Commerce. Cybersecurity Framework | NIST
National Institute of Standards and Technology. (2023). Cybersecurity white papers (CSWP). Computer Security Resource Center. CSWP 53 (Initial Public Draft)
Sridhar, V., Bhatt, M., & Acharya, R. (2015). Cybersecurity education in engineering programs. IEEE Security & Privacy, 13(3), 62–70. A Survey of Data Mining and Machine Learning Methods for Cyber Security Intrusion Detection | IEEE Journals & Magazine
Valkenburg, P. M., & Patti, J. (2018). Adolescents and digital media: From mass entertainment to personalized media. Journal of Adolescent Health, 63(2), 737–744. Full article: A systematic review: the influence of social media on depression, anxiety, and psychological distress in adolescents
Verizon. (2026). Data breach investigations report. Verizon Communications Inc.
Yoo, C., & Huang, H. (2012). Cybersecurity workforce development: Challenges and solutions. IEEE, 1–6. The Quest to Replace Passwords: A Framework for Comparative Evaluation of Web Authentication Schemes | IEEE Conference Publication